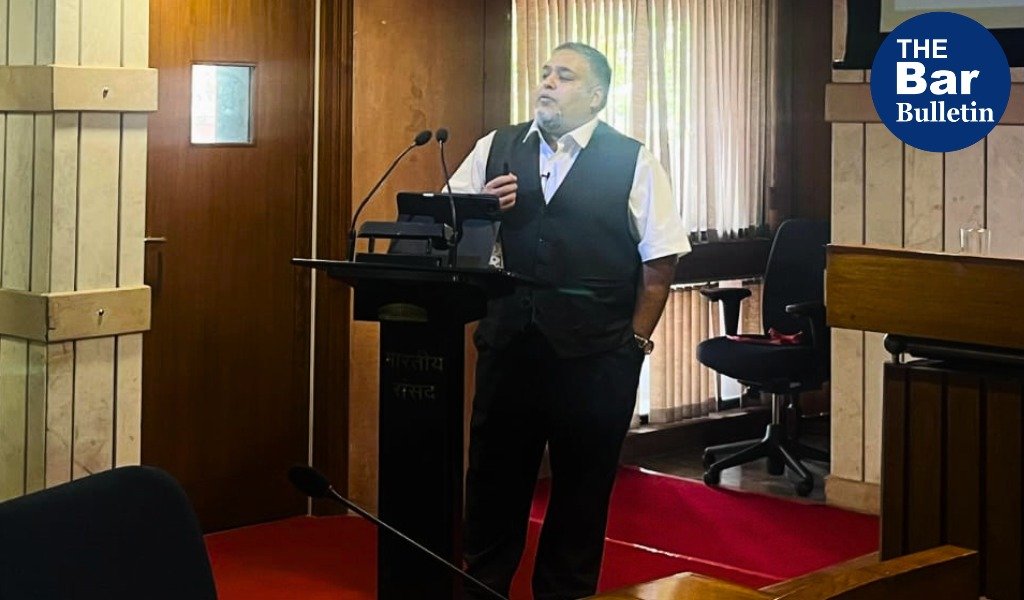
Speaking on October 27, 2026, Dr. Chopra examined India’s evolving legal framework for cybersecurity and data protection. He traced how the Information Technology Act, 2000, the CERT-In Directions of 2022 and the Digital Personal Data Protection Act, 2023 fit together, and what they demand of companies and their boards. His session formed part of the programme’s second day
Opening with the proposition that cybersecurity is no longer merely a technical concern but a corporate responsibility, Dr. Chopra explained that obligations in India currently operate in two phases. The IT Act, the SPDI Rules of 2011 and the CERT-In Directions apply today. The DPDP Act’s core security, processor and breach-notice duties take effect only on May 13, 2027.
He took participants through how the regime developed. The IT Act came into force on October 17, 2000. A 2009 amendment inserted Section 43A, electronic signatures and establishment CERT-In. The SPDI Rules followed in 2011, and the CERT-In 2022 Directions that introduced six-hour incident reporting. He also noted that the Jan Vishwas Act omitted Section 66A, which the Supreme Court had already held unconstitutional in Shreya Singhal v. Union of India (2015) 5 SCC 1 despite which th provision was used by the state mechanism and decriminalized various offences as per the Jan Vishvas Act, 2023.
A central theme of his address was how much wider the law’s protection is becoming. Section 43A of the IT Act protects only ‘sensitive personal data or information’ held by a body corporate. The DPDP Act, by contrast, covers any data about an identifiable individual and any person acting as a Data Fiduciary. It also reaches processing outside India where that processing is connected with offering goods or services to people in India.
Dr. Chopra highlighted the CERT-In requirement that covered entities report incidents such as unauthorized access, ransomware attacks and data breaches within six hours of noticing them. Covered entities must also designate a CERT-In point of contact and keep system logs in India for a rolling 180 days. He pointed out that where details are incomplete, CERT-In’s FAQ allows an entity to report what is known first and add information later.
He also drew attention to a development of particular relevance to banking and real estate practitioners. A notification dated September 26, 2022 amended the First Schedule to the IT Act. As a result, contracts for the sale of immovable property, could now be executed electronically with mechanisms to come. Whether this will displace the established practice of physical execution, he observed, remains to be seen.
Discussing the DPDP Act, he explained that consent must be free, specific, informed, unconditional and unambiguous. It must be given through a clear affirmative action and must be capable of being withdrawn as easily as it was given. He emphasized that outsourcing does not displace a Data Fiduciary’s responsibility for processing done on its behalf.
He noted that the Data Protection Board of India was established in November 2025 but is not yet staffed. Its penalty powers will be significant: up to ₹250 crore for failing to maintain security safeguards, and up to ₹200 crore each for failing to notify a breach and for violations involving children’s data.
Contrasting the two regimes, he explained that Section 43A compensates the person affected, while the DPDP Act imposes penalties that are credited to the Consolidated Fund. He added that civil courts are barred under the new regime.
He cautioned that breach reporting will soon run on parallel clocks: the six-hour CERT-In report, and DPDP intimation to the Board and to affected individuals, with details within 72 hours. He also noted that the CERT-In reporting duty cannot be transferred to a vendor by contract and, under Section 81 of the IT Act, overrides contractual confidentiality.
Also Read AI Cannot Be Allowed to Operate Without Accountability: Sr Adv Shashank Garg at ICPS
He further observed that liability for a single incident can arise on several distinct bases:
- compensation under Section 43A;
- consequences under Section 70B(7);
- company-officer liability under Section 85;
- penalties under the DPDP Act, once its fully enforced.
Concluding on a practical note, he referred to CERT-In’s 15 Elemental Cyber Defense Controls, which set a minimum baseline alongside the binding requirements. He urged participants to watch for phishing red flags: urgency, payment changes and password requests. He noted that Section 66D of the IT Act could broadly cover such conduct.
The session was part of the five-day certificate course on Cyber Security and Artificial Intelligence, being conducted from October 26 to 30, 2026, at the Parliament Library Building, New Delhi. The programme brings together legal professionals, academics, public officials and participants to examine emerging legal, constitutional and policy challenges arising from developments in artificial intelligence and cybersecurity.